In this article
Penetration testing still has to answer a practical question: what can an attacker reach and do in the environment that exists today? AI changes both the pace of testing and the systems that need assessment. Security teams now use AI to accelerate reconnaissance and analysis, while products increasingly expose models, agents, retrieval systems, and tool connections that create new paths for misuse. The useful response is to expand coverage and verify findings, not to treat automation as proof of security.
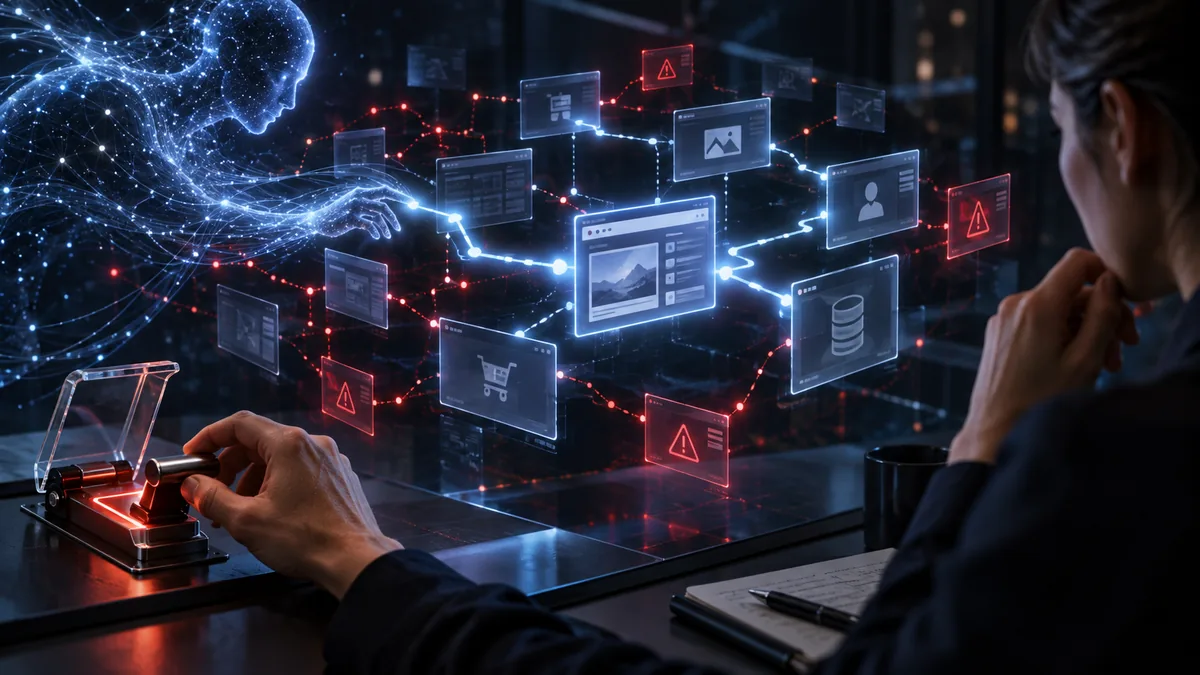
Two things are happening at once. First, artificial intelligence has become a working tool inside penetration testing itself — accelerating reconnaissance, correlating findings, and speeding up reporting. Second, and more consequentially, AI has become a target. Organizations are shipping large language models, AI agents, and retrieval-augmented systems into production faster than their security programs can adapt, and that has opened up a category of vulnerability that didn't exist five years ago. Understanding both sides of that shift is now table stakes for anyone responsible for web application security.
The Gap Between Confidence and Coverage
Two recent industry data points frame the problem well. Synack's 2026 research with Omdia and Informa TechTarget found that while the overwhelming majority of organizations say penetration testing is a priority, they typically test only about a third of their actual attack surface. That gap — between what security teams believe they're covering and what they're actually validating — is the real risk, and it's growing as organizations add cloud services, SaaS integrations, APIs, and AI features faster than test cycles can keep pace.
At the same time, enthusiasm for letting AI run penetration tests unsupervised has cooled considerably. A Cobalt report released in mid-2026 found that only 9% of organizations were willing to rely on AI-powered penetration testing on its own, down sharply from 29% just a year prior. The reason wasn't that AI tooling got worse — it's that security leaders got a clearer, more realistic picture of where autonomous tools still fall short: blind spots, false positives, and testing budgets that can be consumed quickly by AI-driven scanning without producing proportionally better results. The market correction is a healthy one. It reflects a maturing understanding that AI is a force multiplier for skilled testers, not a replacement for them.
What AI Actually Changed About the Pentester's Job
AI can speed up repeatable work such as asset discovery, test-case generation, triage, and report drafting. It does not establish exploitability by itself. Human testers still need to validate business logic, connect findings into realistic attack paths, and distinguish an exploitable weakness from a plausible-sounding alert. Cobalt’s 2026 survey reports that only 9% of respondents favor fully automated penetration testing and that 47% prefer a hybrid model; those are survey results, not a universal measure of tool effectiveness.
The practical effect is a division of labor rather than a handoff. AI-assisted tools are good at breadth — sweeping large environments, flagging anomalies, drafting first-pass findings. Human testers remain essential for depth: understanding business logic, chaining low-severity issues into a real attack path, and exercising the judgment needed to tell a theoretical weakness apart from something an attacker could actually use. The strongest testing programs in 2026 treat this as a layered system, not a choice between “AI” and “human,” and the vendors gaining traction are the ones proving which findings are genuinely exploitable rather than just generating longer vulnerability lists.
The Attack Surface Nobody Was Testing For
The more novel development this year concerns AI as the subject of a security assessment rather than the tool performing one. As organizations embed LLMs, copilots, and autonomous agents into customer-facing products, they've introduced a set of vulnerabilities that traditional web application testing was never designed to catch. AI-specific penetration testing now evaluates large language models, AI agents, retrieval-augmented generation pipelines, and Model Context Protocol servers against adversarial misuse, covering risks like prompt injection, jailbreaking, training data or system prompt exfiltration, agentic action-chaining exploits, and poisoning of retrieval knowledge bases — none of which map cleanly onto conventional vulnerability classes like SQL injection or broken authentication.
OWASP’s current LLM Application Top 10 is the 2025 edition. It ranks prompt injection first and lists excessive agency at number six. OWASP also publishes a separate Top 10 for Agentic Applications. These frameworks describe persistent risks: untrusted instructions can influence model behavior, and excessive tools, permissions, or autonomy can turn that behavior into consequential actions. Treat them as assessment guides, not a guarantee that a checklist alone covers a deployment.
For teams building or deploying AI features, this means a conventional web app pentest — even a thorough one — will miss an entire layer of exploitable behavior. Testing whether an AI system can be manipulated into leaking a system prompt, misusing a connected tool, or taking an unintended action on a user's behalf requires expertise and methodology distinct from classic OWASP Top 10 web testing.
Old Frameworks, New Application
It's worth noting what hasn't changed. Established methodologies — PTES, NIST SP 800-115, OSSTMM, and the OWASP Testing Guide — still provide the structural backbone for evaluating applications, networks, and cloud infrastructure, and they aren't being discarded. What's changed is that AI-enabled systems sit on top of that same infrastructure and inherit its risks while adding entirely new ones on top: the API serving your LLM still needs the same authentication and access-control scrutiny it always did, even as the model behind it needs a separate assessment for prompt-level manipulation.
This is also why the “periodic, point-in-time” model of pentesting is under pressure independent of the AI security conversation. Software delivery has sped up — especially with AI-assisted development shortening release cycles — and a security assessment that only happens once a year increasingly represents a snapshot of an environment that no longer exists by the time the report lands. Continuous, externally verifiable testing that keeps pace with how fast public-facing applications actually change is becoming less of a nice-to-have and more of an expectation.
What This Means for Your Organization
For security and engineering leaders, the current priorities are straightforward:
- Don't assume your last pentest covered your current attack surface. With most organizations validating only a fraction of it, treat scope as something that needs to expand alongside your infrastructure and product surface — not something set once and revisited annually.
- Separate “AI-assisted testing” from “AI-run testing.” The data supports AI as an accelerant inside a professionally managed engagement. It doesn't yet support letting autonomous tools operate unsupervised against production systems, particularly anything customer-facing.
- If you've shipped AI features, they need their own assessment. Prompt injection, excessive agency, and tool-chaining risks won't surface in a conventional web application test. If your product includes a chatbot, copilot, or agent with access to real data or real actions, that surface needs dedicated evaluation.
- Verified, non-destructive external testing remains the safest starting point. Before authenticated or higher-risk testing enters the conversation, a rigorous external assessment against your live, verified web applications establishes a real baseline of what an outside attacker can actually see and reach — without the operational risk of exploit attempts against production systems.
Penetration testing remains a way to verify what is exploitable in a defined scope. In 2026, that scope needs to include the systems around AI features as well as the model-facing behavior itself. Revisit it when products, integrations, permissions, or exposed assets change, and require evidence that reported findings can be reproduced and safely addressed.
Sources and further reading
Synack and Omdia 2026 State of Agentic AI in Pentesting
Cobalt AI and Pentesting Pulse Report 2026