In this article
Notepad++ disclosed a compromise affecting update infrastructure on February 2, 2026. Palo Alto Networks Unit 42 later reported that attackers had compromised the shared hosting environment between June and December 2025 and selectively redirected some update traffic. The project’s source code and ordinary release binaries were not described as compromised. Researchers linked the activity to Lotus Blossom and reported targeted delivery chains, including a Chrysalis backdoor. The incident is a present-day reminder that trust in a software publisher also depends on its hosting and update path.
How It Worked
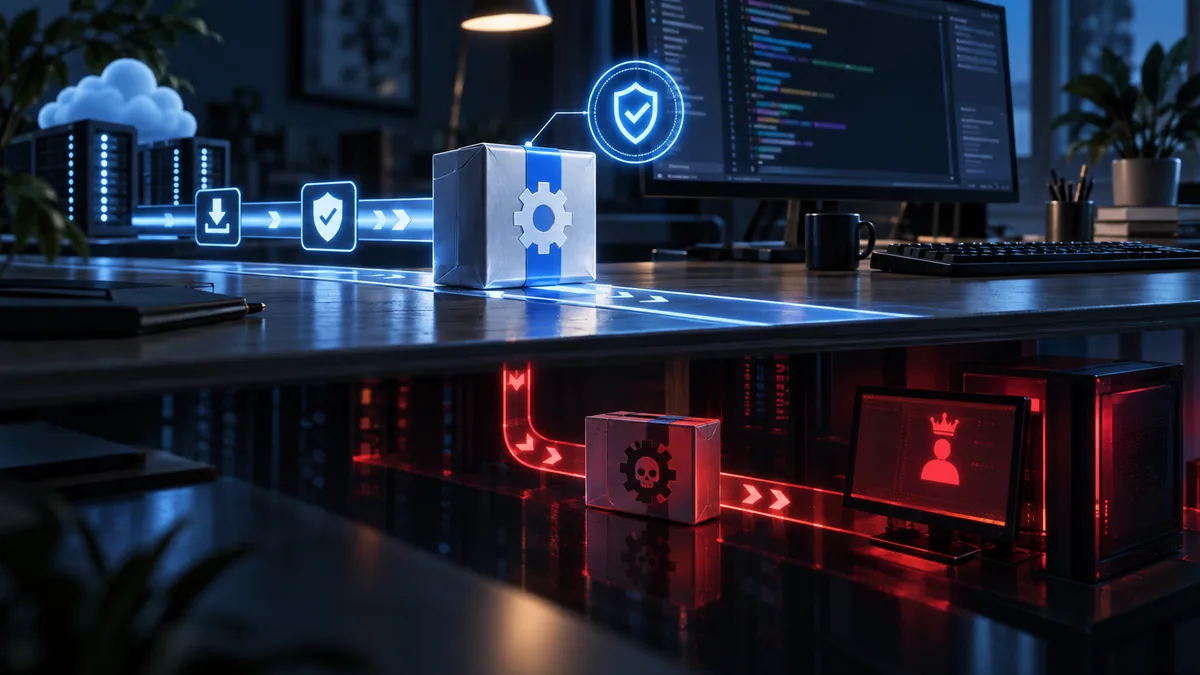
Investigators described an infrastructure-level compromise at the hosting provider, which allowed selective redirection of update requests. That differs from a source-code or package-registry compromise: the attackers targeted delivery to chosen systems while many users continued receiving legitimate updates. Keep these distinctions clear when deciding whether an endpoint may have been exposed.
For the handful of systems selected, the malicious update delivered a payload through DLL sideloading — abusing renamed, legitimate executables to load a previously undocumented backdoor researchers named Chrysalis, the latest evolution in a malware lineage that traces back through Lotus Blossom's earlier tools Elise and Sagerunex. Chrysalis was built for stealth and longevity: encrypted, deliberately low-frequency HTTPS communications designed to resemble ordinary API traffic, structured command-and-control, and advanced loader obfuscation with API hashing to frustrate analysis.
Why Six Months
Selective targeting can reduce the signals defenders expect from a mass compromise. A low volume of malicious deliveries may not create a visible spike, so update channels and their endpoint behavior need monitoring even when the software itself is approved.
Who Was Actually Hit
Initial findings identified a limited set of affected organizations and individuals; Unit 42’s February 2026 follow-up described additional organizations across more sectors and regions. These are researchers’ observed cases, not a complete count of all affected users. Prioritize review for systems that used the updater during the reported exposure window and follow the project’s and investigators’ current guidance.
The Broader Lesson: Trusted Tools Are Still a Blind Spot
Organizations commonly review software at approval and installation, then allow updater processes to operate with limited scrutiny. The Notepad++ incident shows why both the software and its delivery path need ongoing verification. Track approved versions, verify signatures and hashes through trusted channels, and investigate updater behavior that falls outside its normal destinations or process chain.
What Security Testing Would Catch
- Continuous update-channel verification, not just install-time vetting. Validating code signatures and hashes against known-good releases on an ongoing basis catches a compromised distribution point that initial software approval never will.
- Behavioral baselining of updater processes specifically. Because updaters are commonly allowlisted, they deserve dedicated monitoring of their own — what a process like GUP.exe should normally contact, how often, and at what payload size — so a deviation actually stands out.
- Red-teaming trusted-tool abuse paths. Simulating whether a compromised update channel for an already-approved tool could reach privileged developer or sysadmin workstations undetected tests exactly the scenario Lotus Blossom exploited.
- DLL sideloading detection testing. Since Chrysalis relied on sideloading through renamed legitimate executables, endpoint testing should specifically probe for this technique on technical staff workstations, not just generic malware signatures.
- Risk classification of developer and administrative tooling. Widely deployed utilities installed on privileged technical staff's machines warrant a higher monitoring tier precisely because of who they're likely to be running on.
What This Means for Your Organization
- Treat “already approved” software as an ongoing trust decision, not a one-time gate. Periodically validate that the update channel for tools you approved months or years ago hasn't been quietly redirected since.
- Give updater processes their own behavioral baseline. An allowlisted process is still worth monitoring — it's just monitored differently, by watching for deviation from its normal pattern rather than blocking it outright.
- Prioritize security attention on developer and sysadmin tooling specifically. These tools sit on your most privileged endpoints, making them disproportionately valuable targets regardless of how mundane they seem.
- Don't equate low visibility with low risk. The quietest supply chain compromises — selective, narrowly targeted, low-volume — are often more dangerous than the loud ones, precisely because they're built to avoid the signals your monitoring is tuned to catch.
- Build update-channel and sideloading abuse scenarios into red-team exercises. Testing whether your environment would catch this specific pattern is far more useful than assuming your existing controls already cover it.
The current control gap lies between approving a tool and continuing to verify how it reaches endpoints. Review software update channels as part of supply-chain risk management, prioritize tools on privileged workstations, and preserve enough telemetry to investigate targeted delivery. Follow vendor and researcher advisories for affected versions and remediation steps.
Sources and further reading
Notepad++ February 2026 security announcement